
AtlassianSecurity incident

Atlassian Rovo AI Vulnerability Lets Attackers Steal Enterprise Data With a Single Click
What happened

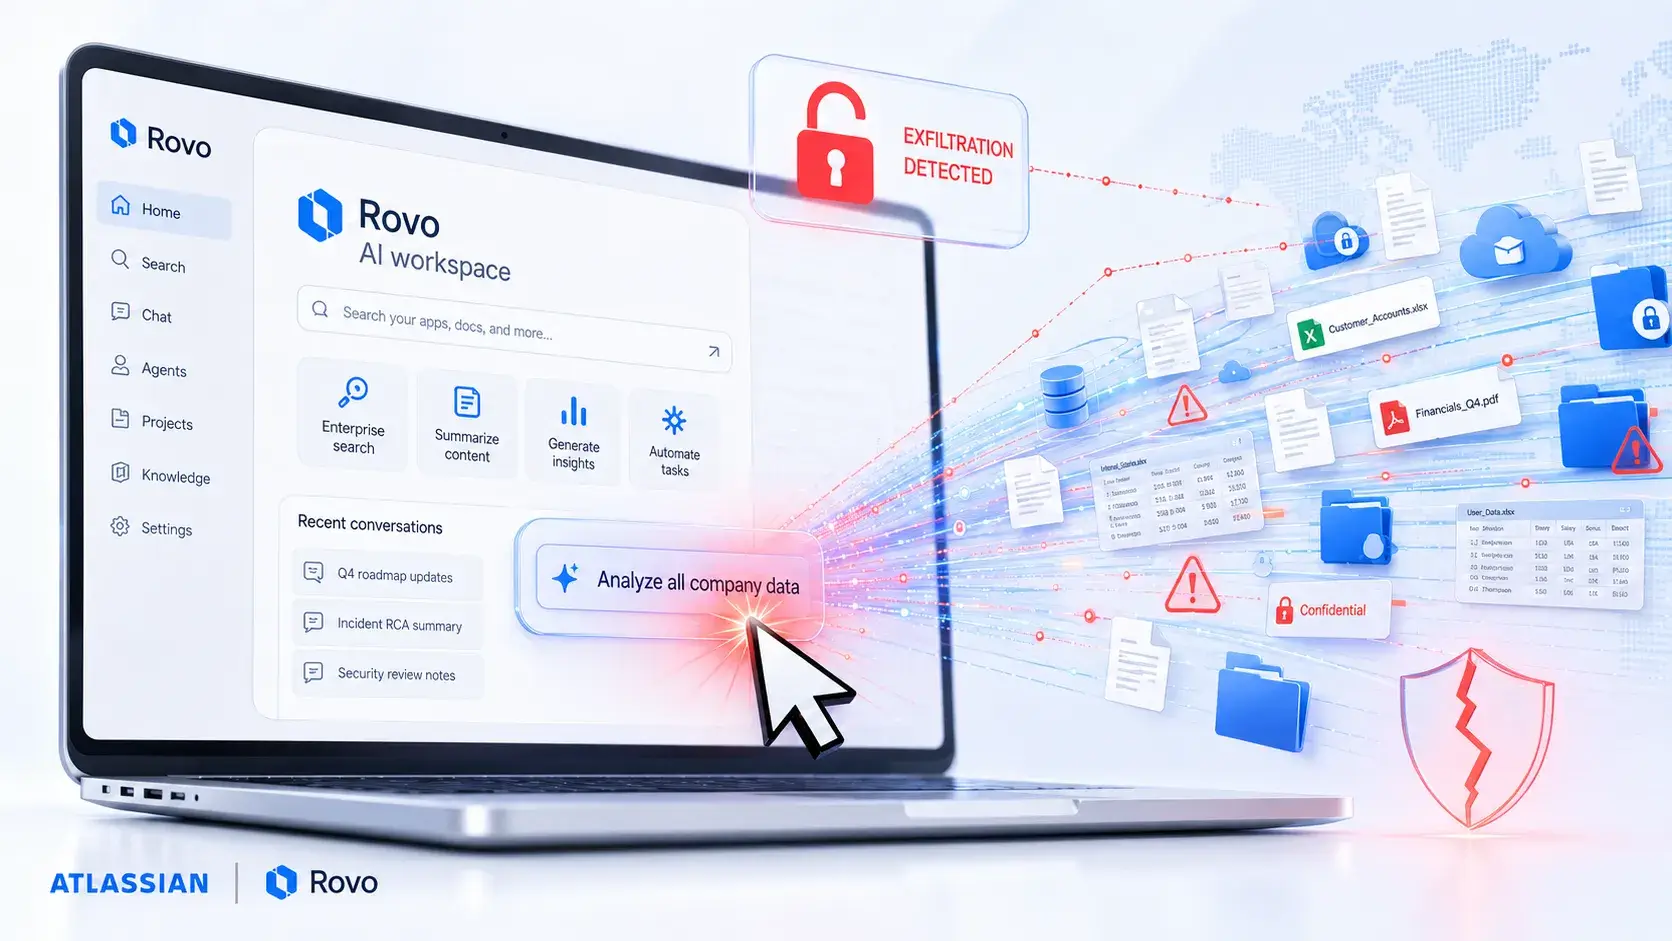
Atlassian's Rovo AI assistant was found to have a vulnerability, named RovoBlast, that could allow attackers to expose sensitive enterprise data through a single malicious link.

Source

Article excerpt

Highlighted: the sentence this signal was extracted from

RovoBlast is a recently disclosed vulnerability affecting Atlassian's Rovo AI assistant that allows attackers to expose sensitive enterprise data through a single malicious link. According to Varonis Threat Labs, the vulnerability exploits Rovo's handling of URL-supplied prompts, enabling attackers to inject malicious instructions into an authenticated user's AI session. The attack does not require traditional permission bypasses, jailbreaks, or exploits of the victim's account. Instead, it exploits a parameter-to-prompt (P2P) weakness: Rovo treats text embedded in a URL as a pre-filled chat instruction within a user's trusted session. Researchers named the issue RovoBlast due to the potentially extensive impact created by Rovo's integrations and agent capabilities. A crafted link using the `rovoChatPrompt` parameter could open Rovo Chat with attacker-provided instructions preloaded. An example link follows this pattern: When a logged-in employee clicks the link, Rovo may interpret the supplied content as an instruction rather than untrusted external input. Varonis indicated that this creates a low-friction pathway for attackers, allowing the assistant to search, summarize, and possibly move organizational data without obvious warnings or confirmation prompts. Rovo is designed to serve as an AI layer across Atlassian products, including Jira, Confluence, and Bitbucket. It...

Keep reading with a free account

The rest of this article, and every signal for Atlassian, is in your free account.

Extracted by Autobound

From the Signal API record
Event
Security incident

What this signalsA breach often leads to new security spend.

Product
Rovo AI

More security incident signals at other companies

The full record

From the Signal API record

Details

Issue named
RovoBlast vulnerability exploiting URL-supplied prompts (P2P weakness)

Topics and mentions

Product tags

  • future tech
  • general technology

Extraction

Confidence
95%
Detected
Aug 10, 2026
signal_type
news
signal_subtype
security_incident

Use this data

Get every security incident signal for Atlassian and the companies you sell to, in the tools you already use.

  1. Ask Claude about it

    Connect Autobound to Claude, Claude Code or Cursor with MCP. Then ask: “What changed at Atlassian this week?”

  2. Send it to your own tools

    The Signal API returns security incident signals for any list of companies as JSON, for your CRM, warehouse or app.

  3. Try it free

    Sign up and spend your free credits on the companies you sell to.

    Start Free1,000 free credits

The API returns more than this page shows

This page shows a preview. The full news record in the Signal API and MCP can also have these 8 fields. Some fields are empty for some signals.

Company

  • linkedin_urlValue in the API
  • industriesValue in the API
  • employee_count_lowValue in the API
  • employee_count_highValue in the API
  • revenueValue in the API
  • descriptionValue in the API

Signal

  • signal_nameValue in the API
  • associationValue in the API
Show the full JSONThe record on this page and the API request

GET /v1/signals/dff1e8ef-1387-579d-45e4-b83c9c2eb056 returns this record as JSON. POST /v1/companies/enrich returns every signal for atlassian.com.

{
  "signal_id": "dff1e8ef-1387-579d-45e4-b83c9c2eb056",
  "signal_type": "news",
  "signal_subtype": "security_incident",
  "detected_at": "2026-08-10T11:08:15+00:00",
  "company": {
    "name": "Atlassian",
    "domain": "atlassian.com"
  },
  "data": {
    "url": "https://gbhackers.com/atlassian-rovo-ai-vulnerability/",
    "title": "Atlassian Rovo AI Vulnerability Lets Attackers Steal Enterprise Data With a Single Click - gbhackers.com",
    "excerpt": "RovoBlast is a recently disclosed vulnerability affecting Atlassian’s Rovo AI assistant that allows attackers to expose sensitive enterprise data through a single malicious link. According to Varonis Threat Labs, the vulnerability exploits Rovo’s handling of URL-supplied prompts, enabling attackers to inject malicious instructions into an authenticated user’s AI session. The attack does not require traditional permission bypasses, jailbreaks, or exploits of the victim’s account. Instead, it exploits a parameter-to-prompt (P2P) weakness: Rovo treats text embedded in a URL as a pre-filled chat instruction within a user’s trusted session. Researchers named the issue RovoBlast due to the potentially extensive impact created by Rovo’s integrations and agent capabilities. A crafted link using the `rovoChatPrompt` parameter could open Rovo Chat with attacker-provided instructions preloaded. An example link follows this pattern: When a logged-in employee clicks the link, Rovo may interpret the supplied content as an instruction rather than untrusted external input. Varonis indicated that this creates a low-friction pathway for attackers, allowing the assistant to search, summarize, and possibly move organizational data without obvious warnings or confirmation prompts. Rovo is designed to serve as an AI layer across Atlassian products, including Jira, Confluence, and Bitbucket. It also...",
    "product": "Rovo AI",
    "summary": "Atlassian's Rovo AI assistant was found to have a vulnerability, named RovoBlast, that could allow attackers to expose sensitive enterprise data through a single malicious link.",
    "planning": false,
    "image_url": "https://gbhackers.com/wp-content/uploads/2026/08/fbb4a136-3fd9-4223-a6bd-126a9ef263d0-1.webp",
    "confidence": 0.95,
    "product_data": {
      "name": "Rovo AI",
      "full_text": "Atlassian’s Rovo AI assistant",
      "fuzzy_match": false
    },
    "product_tags": [
      "future_tech",
      "general_technology"
    ],
    "published_at": "2026-08-10T11:08:15Z",
    "vulnerability": "RovoBlast vulnerability exploiting URL-supplied prompts (P2P weakness)",
    "article_sentence": "RovoBlast is a recently disclosed vulnerability affecting Atlassian’s Rovo AI assistant that allows attackers to expose sensitive enterprise data through a single malicious link."
  }
}

Long text fields are shortened on this page.

Looking up one signal by its id is free. Enrich costs 2 credits per signal returned; a call with no results is free.